
Plik PS1 to skrypt lub polecenie cmdlet używane przez program Windows PowerShell .
W tym przewodniku dowiesz się, jak dodać lub usunąć niestandardowe menu Edytuj lub Uruchom za pomocą do menu kontekstowego plików .ps1 programu PowerShell dla wszystkich użytkowników systemu Windows 10 .
Menu kontekstowe Edytuj lub Uruchom za pomocą zawiera następujące elementy dla plików PS1:
- Uruchom z PowerShellem
- Uruchom z PowerShellem jako administrator
- Uruchom z PowerShellem 7
- Uruchom z PowerShell 7 jako administrator
- Edytuj za pomocą PowerShell ISE
- Edytuj za pomocą PowerShell ISE jako administrator
- Edytuj za pomocą PowerShell ISE (x86)
- Edytuj za pomocą programu PowerShell ISE (x86) jako administrator
- Edytuj za pomocą Notatnika
- Edytuj za pomocą Notatnika jako administrator
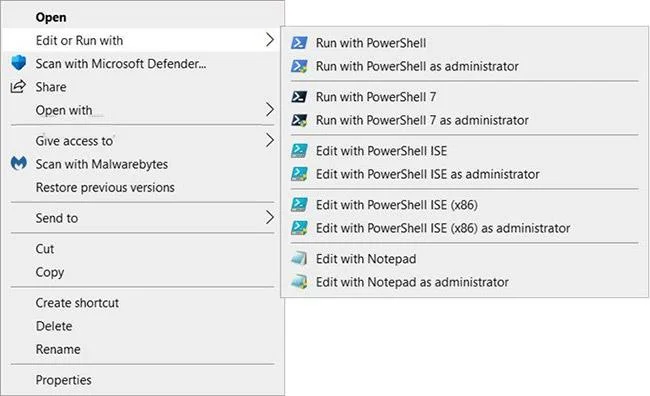
Dodaj opcję „Edytuj lub uruchom za pomocą” do menu wyświetlanego prawym przyciskiem myszy pliku PS1 w systemie Windows 10
Jak dodać opcję „Edytuj lub uruchom za pomocą” do menu wyświetlanego prawym przyciskiem myszy pliku PS1 w systemie Windows 10
Oto jak:
1. Wykonaj krok 2 (dodaj – kliknięcie prawym przyciskiem myszy), krok 3 (dodaj – Shift + kliknięcie prawym przyciskiem myszy) lub krok 4 (usuń) poniżej, w zależności od tego, co chcesz zrobić.
2. Aby dodać menu kontekstowe pliku PS1 „Edytuj lub uruchom z” (wystarczy kliknąć prawym przyciskiem myszy, aby wyświetlić), pobierz plik Add_Edit_or_Run_with_to_PS1_context_menu.reg .
Zawartość pliku REG) - Kod:
Windows Registry Editor Version 5.00

[-HKEY_CLASSES_ROOT\.ps1]

[HKEY_CLASSES_ROOT\.ps1]
@="Microsoft.PowerShellScript.1"

[-HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1]

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1]
"EditFlags"=dword:00020000
"FriendlyTypeName"=hex(2):40,00,22,00,25,00,73,00,79,00,73,00,74,00,65,00,6d,\
  00,72,00,6f,00,6f,00,74,00,25,00,5c,00,73,00,79,00,73,00,74,00,65,00,6d,00,\
  33,00,32,00,5c,00,77,00,69,00,6e,00,64,00,6f,00,77,00,73,00,70,00,6f,00,77,\
  00,65,00,72,00,73,00,68,00,65,00,6c,00,6c,00,5c,00,76,00,31,00,2e,00,30,00,\
  5c,00,70,00,6f,00,77,00,65,00,72,00,73,00,68,00,65,00,6c,00,6c,00,2e,00,65,\
  00,78,00,65,00,22,00,2c,00,2d,00,31,00,30,00,33,00,00,00

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\DefaultIcon]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell_ise.exe\",1"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell]
@="Open"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Open\Command]
@="\"C:\\Windows\\System32\\notepad.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with]
"MUIVerb"="Edit or Run with"
"Extended"=-
"SubCommands"=""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\001flyout]
"MUIVerb"="Run with PowerShell"
"Icon"="powershell.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\001flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell.exe\" \"-Command\" \"if((Get-ExecutionPolicy ) -ne 'AllSigned') { Set-ExecutionPolicy -Scope Process Bypass }; & '%1'\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\002flyout]
"MUIVerb"="Run with PowerShell as administrator"
"HasLUAShield"=""
"Icon"="powershell.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\002flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell.exe\" \"-Command\" \"\"& {Start-Process PowerShell.exe -ArgumentList '-ExecutionPolicy RemoteSigned -File \\\"%1\\\"' -Verb RunAs}\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\003flyout]
"MUIVerb"="Run with PowerShell 7"
"Icon"="pwsh.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\003flyout\Command]
@="\"C:\\Program Files\\PowerShell\\7\\pwsh.exe\" \"-Command\" \"if((Get-ExecutionPolicy ) -ne 'AllSigned') { Set-ExecutionPolicy -Scope Process Bypass }; & '%1'\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\004flyout]
"MUIVerb"="Run with PowerShell 7 as administrator"
"HasLUAShield"=""
"Icon"="pwsh.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\004flyout\Command]
@="\"C:\\Program Files\\PowerShell\\7\\pwsh.exe\" \"-Command\" \"\"& {Start-Process pwsh.exe -ArgumentList '-ExecutionPolicy RemoteSigned -File \\\"%1\\\"' -Verb RunAs}\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\005flyout]
"MUIVerb"="Edit with PowerShell ISE"
"Icon"="powershell_ise.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\005flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell_ise.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\006flyout]
"MUIVerb"="Edit with PowerShell ISE as administrator"
"HasLUAShield"=""
"Icon"="powershell_ise.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\006flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start PowerShell_ISE.exe \"\"%1\"\"'  -Verb RunAs\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\007flyout]
"MUIVerb"="Edit with PowerShell ISE (x86)"
"Icon"="powershell_ise.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\007flyout\Command]
@="\"C:\\WINDOWS\\syswow64\\WindowsPowerShell\\v1.0\\powershell_ise.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\008flyout]
"MUIVerb"="Edit with PowerShell ISE (x86) as administrator"
"HasLUAShield"=""
"Icon"="powershell_ise.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\008flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start C:\\WINDOWS\\syswow64\\WindowsPowerShell\\v1.0\\powershell_ise.exe \"\"%1\"\"'  -Verb RunAs\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\009flyout]
"MUIVerb"="Edit with Notepad"
"Icon"="notepad.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\009flyout\Command]
@="\"C:\\Windows\\System32\\notepad.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\010flyout]
"MUIVerb"="Edit with Notepad as administrator"
"HasLUAShield"=""
"Icon"="notepad.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\010flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start C:\\Windows\\System32\\notepad.exe \"\"%1\"\"'  -Verb RunAs\""
3. Aby dodać menu kontekstowe pliku PS1 „Edytuj lub Uruchom za pomocą” (naciśnij Shift + kliknij prawym przyciskiem myszy, aby wyświetlić), pobierz plik Add_Shift + Edit_or_Run_with_to_PS1_context_menu.reg .
Zawartość REG - pliku kodu:
Windows Registry Editor Version 5.00

[-HKEY_CLASSES_ROOT\.ps1]

[HKEY_CLASSES_ROOT\.ps1]
@="Microsoft.PowerShellScript.1"

[-HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1]

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1]
"EditFlags"=dword:00020000
"FriendlyTypeName"=hex(2):40,00,22,00,25,00,73,00,79,00,73,00,74,00,65,00,6d,\
  00,72,00,6f,00,6f,00,74,00,25,00,5c,00,73,00,79,00,73,00,74,00,65,00,6d,00,\
  33,00,32,00,5c,00,77,00,69,00,6e,00,64,00,6f,00,77,00,73,00,70,00,6f,00,77,\
  00,65,00,72,00,73,00,68,00,65,00,6c,00,6c,00,5c,00,76,00,31,00,2e,00,30,00,\
  5c,00,70,00,6f,00,77,00,65,00,72,00,73,00,68,00,65,00,6c,00,6c,00,2e,00,65,\
  00,78,00,65,00,22,00,2c,00,2d,00,31,00,30,00,33,00,00,00

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\DefaultIcon]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell_ise.exe\",1"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell]
@="Open"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Open\Command]
@="\"C:\\Windows\\System32\\notepad.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with]
"MUIVerb"="Edit or Run with"
"Extended"=""
"SubCommands"=""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\001flyout]
"MUIVerb"="Run with PowerShell"
"Icon"="powershell.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\001flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell.exe\" \"-Command\" \"if((Get-ExecutionPolicy ) -ne 'AllSigned') { Set-ExecutionPolicy -Scope Process Bypass }; & '%1'\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\002flyout]
"MUIVerb"="Run with PowerShell as administrator"
"HasLUAShield"=""
"Icon"="powershell.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\002flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell.exe\" \"-Command\" \"\"& {Start-Process PowerShell.exe -ArgumentList '-ExecutionPolicy RemoteSigned -File \\\"%1\\\"' -Verb RunAs}\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\003flyout]
"MUIVerb"="Run with PowerShell 7"
"Icon"="pwsh.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\003flyout\Command]
@="\"C:\\Program Files\\PowerShell\\7\\pwsh.exe\" \"-Command\" \"if((Get-ExecutionPolicy ) -ne 'AllSigned') { Set-ExecutionPolicy -Scope Process Bypass }; & '%1'\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\004flyout]
"MUIVerb"="Run with PowerShell 7 as administrator"
"HasLUAShield"=""
"Icon"="pwsh.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\004flyout\Command]
@="\"C:\\Program Files\\PowerShell\\7\\pwsh.exe\" \"-Command\" \"\"& {Start-Process pwsh.exe -ArgumentList '-ExecutionPolicy RemoteSigned -File \\\"%1\\\"' -Verb RunAs}\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\005flyout]
"MUIVerb"="Edit with PowerShell ISE"
"Icon"="powershell_ise.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\005flyout\Command]
@="\"C:\\Windows\\System32\\WindowsPowerShell\\v1.0\\powershell_ise.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\006flyout]
"MUIVerb"="Edit with PowerShell ISE as administrator"
"HasLUAShield"=""
"Icon"="powershell_ise.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\006flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start PowerShell_ISE.exe \"\"%1\"\"'  -Verb RunAs\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\007flyout]
"MUIVerb"="Edit with PowerShell ISE (x86)"
"Icon"="powershell_ise.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\007flyout\Command]
@="\"C:\\WINDOWS\\syswow64\\WindowsPowerShell\\v1.0\\powershell_ise.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\008flyout]
"MUIVerb"="Edit with PowerShell ISE (x86) as administrator"
"HasLUAShield"=""
"Icon"="powershell_ise.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\008flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start C:\\WINDOWS\\syswow64\\WindowsPowerShell\\v1.0\\powershell_ise.exe \"\"%1\"\"'  -Verb RunAs\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\009flyout]
"MUIVerb"="Edit with Notepad"
"Icon"="notepad.exe"
"CommandFlags"=dword:00000020

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\009flyout\Command]
@="\"C:\\Windows\\System32\\notepad.exe\" \"%1\""


[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\010flyout]
"MUIVerb"="Edit with Notepad as administrator"
"HasLUAShield"=""
"Icon"="notepad.exe"

[HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with\shell\010flyout\Command]
@="PowerShell -windowstyle hidden -Command \"Start-Process cmd -ArgumentList '/s,/c,start C:\\Windows\\System32\\notepad.exe \"\"%1\"\"'  -Verb RunAs\""
4. Aby usunąć menu kontekstowe pliku PS1 „Edytuj lub uruchom za pomocą”, pobierz plik Remove_Edit_or_Run_with_from_PS1_context_menu.reg .
Zawartość REG - pliku kodu:
Windows Registry Editor Version 5.00

[-HKEY_CLASSES_ROOT\Microsoft.PowerShellScript.1\Shell\Edit-Run-with]
5. Zapisz plik .reg na pulpicie.
6. Kliknij dwukrotnie pobrany plik .reg , aby go scalić.
7. Po wyświetleniu monitu kliknij opcję Uruchom > Tak (UAC) > Tak > OK, aby zatwierdzić połączenie.
8. Teraz możesz usunąć pobrany plik .reg, jeśli chcesz.
Mam nadzieję, że odniesiesz sukces.





